
Product cybersecurity in Europe
Products evolve, and so do the regulations
Cybersecurity has become a major issue with the rise of malware, firmware vulnerabilities and attacks on connected devices. To protect users, the European Union has adopted several regulations that strengthen the security of products and their associated digital services. They apply to all products placed on the EU market, including those of Swiss manufacturers; Switzerland takes over some of these rules, for example the cybersecurity requirements of the Radio Equipment Directive.
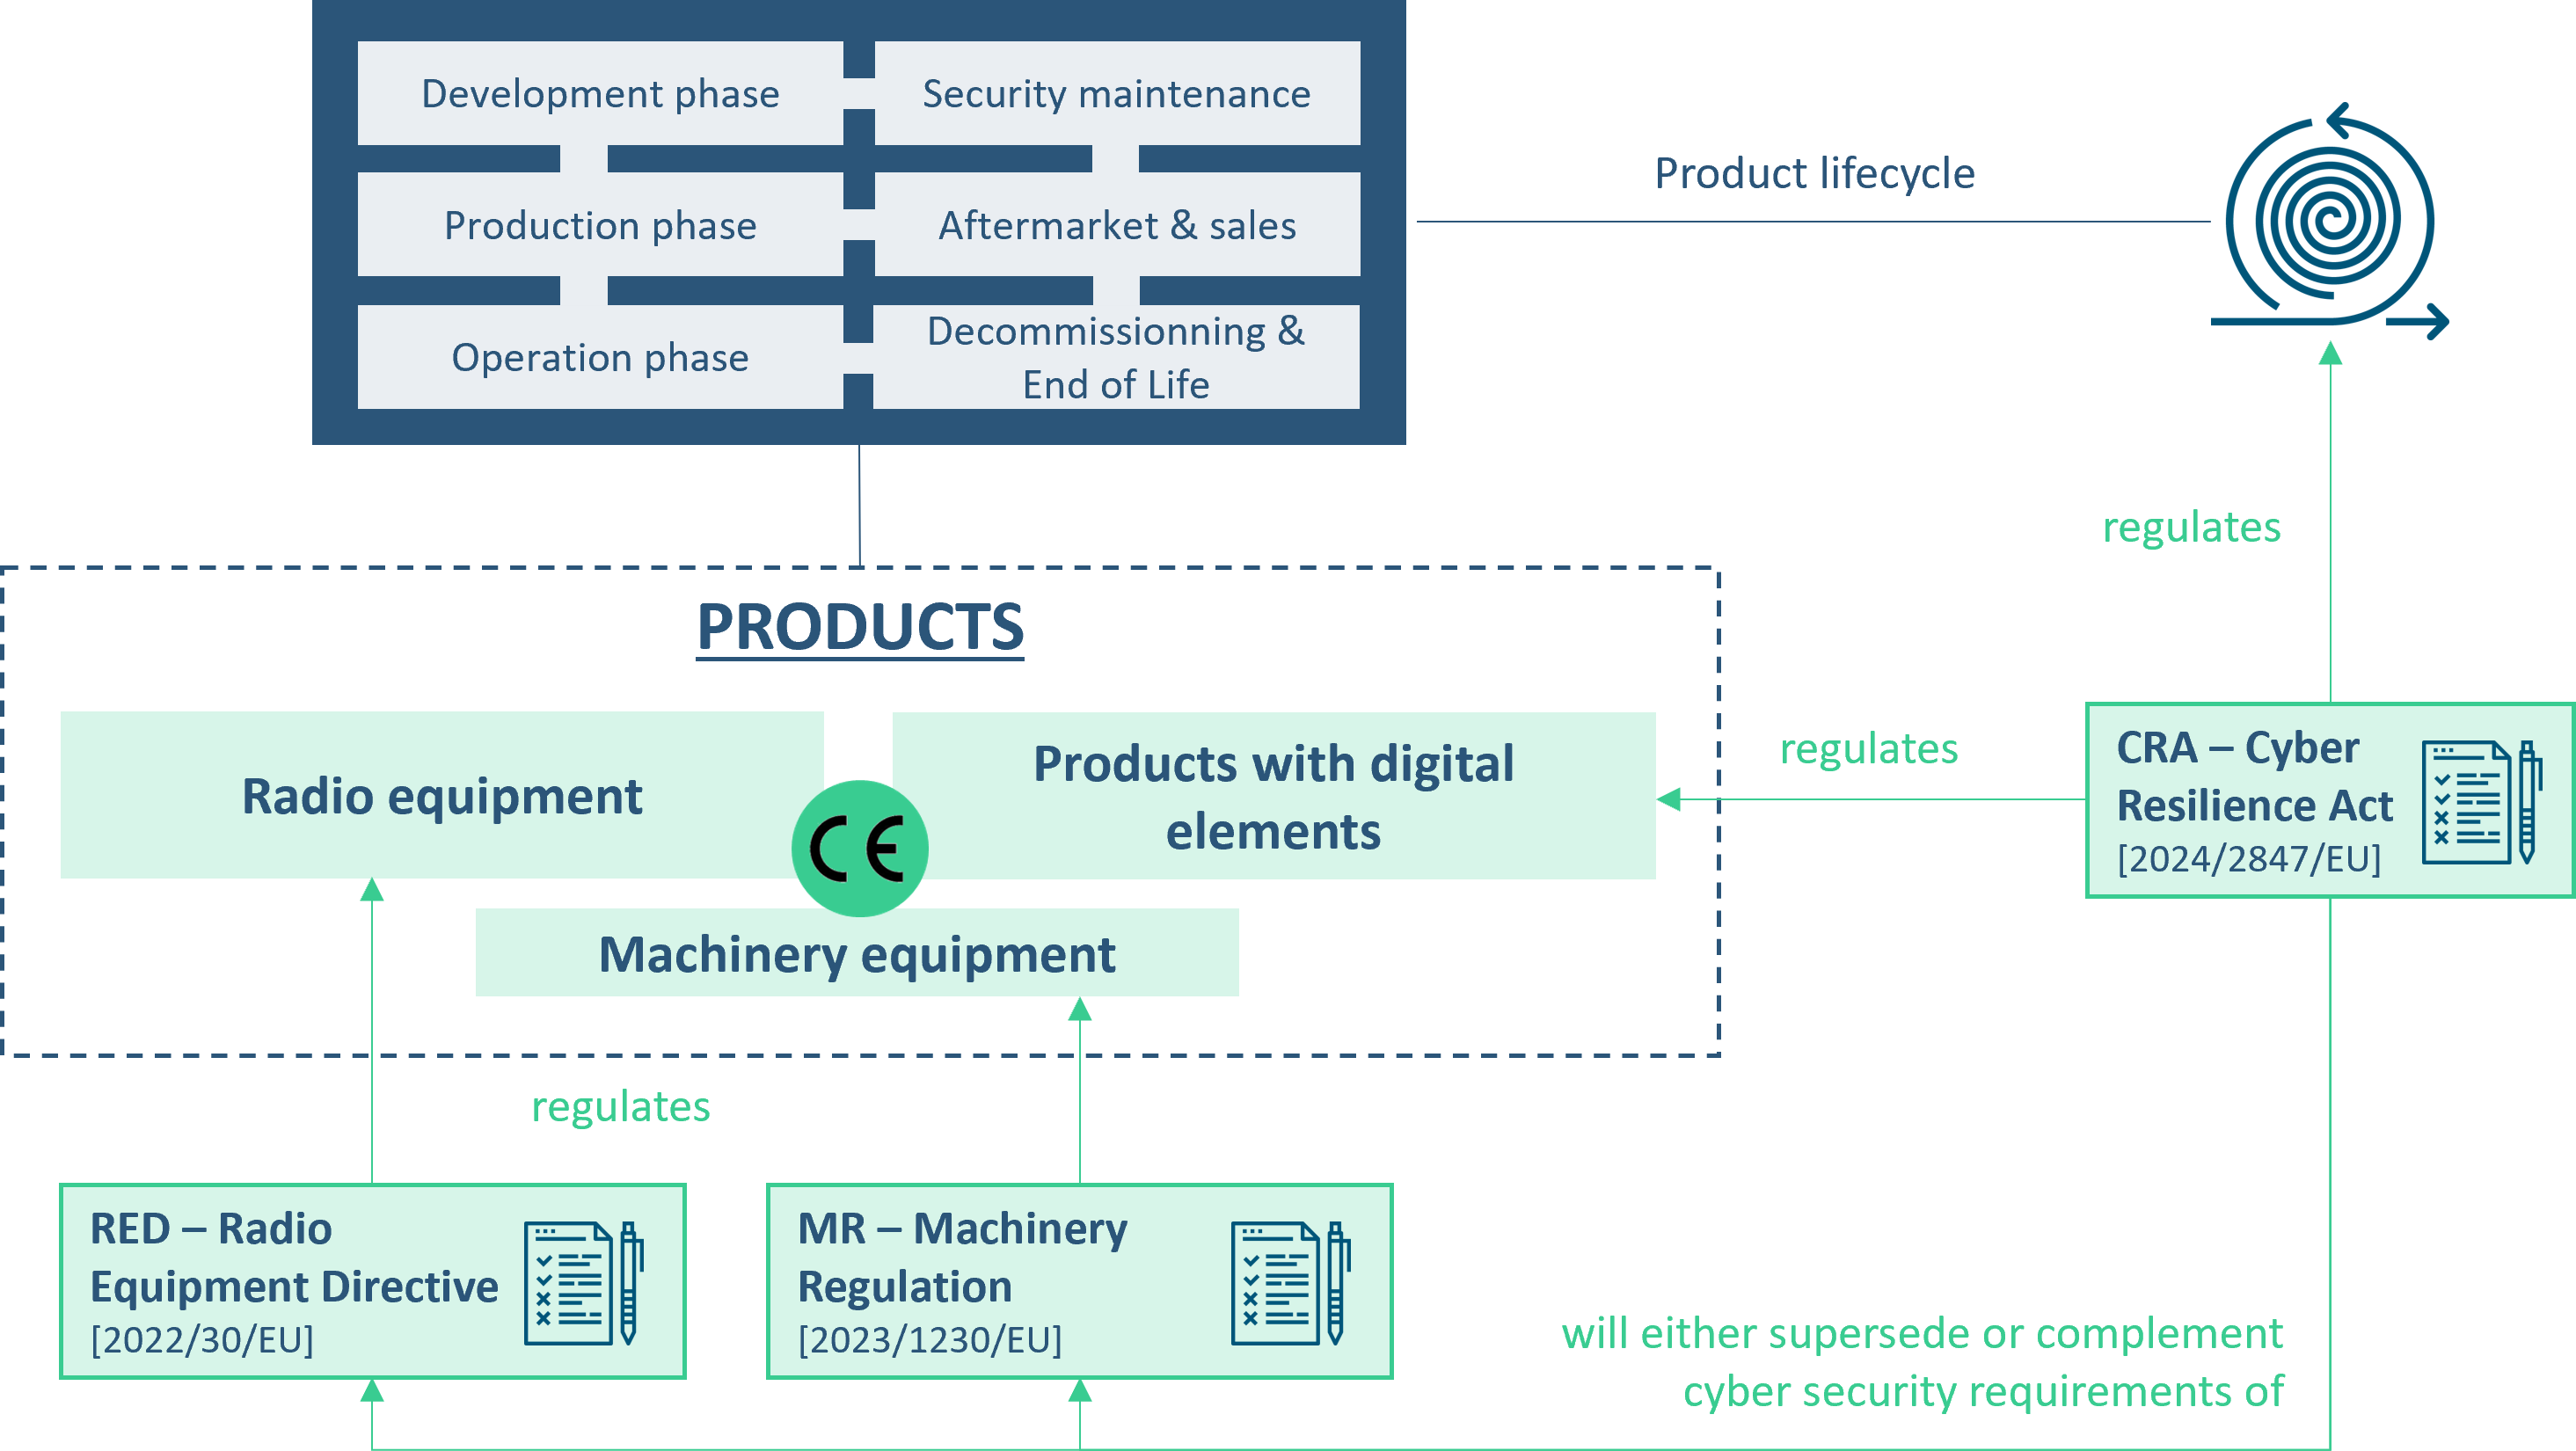
This page presents three regulations that concern different types of products: the Cyber Resilience Act (CRA), the delegated act of the Radio Equipment Directive (RED) and the Machinery Regulation (MR). The diagram below shows how they relate; the questionnaire that follows helps you identify which ones may apply to your product.
Cybersecurity
Cyber Resilience Act (CRA)
Regulation (EU) 2024/2847 is the core of the new cybersecurity obligations for manufacturers, importers and distributors of products with digital elements. Reporting of actively exploited vulnerabilities and severe incidents applies since 11 September 2026; all other requirements, from secure development to vulnerability handling over the whole life cycle, apply from 11 December 2027.
Functional SafetyCybersecurity
Radio Equipment Directive (RED) – delegated act
Delegated Regulation (EU) 2022/30 adds cybersecurity requirements to Directive 2014/53/EU for radio equipment: protection of networks, of personal data and privacy, and protection against fraud for products that process financial transactions. It applies since 1 August 2025; the harmonised standards EN 18031-1, -2 and -3 can be used to demonstrate compliance.
Functional SafetyCybersecurityAI
Machinery Regulation (MR)
Regulation (EU) 2023/1230 replaces Directive 2006/42/EC and applies from 20 January 2027. It adds requirements on safety-related control systems and software, protection against corruption, including cyberattacks, artificial intelligence and human–machine interaction. For cybersecurity, its requirements work together with those of the CRA.
Which regulations apply to my product?
This six-step questionnaire gives you a first indication of the regulations that may apply to your product. It does not replace a detailed analysis of your case.
Note: a product with digital elements is a hardware or software product, including its remote data processing solutions, as well as hardware or software components placed on the market separately.
Questions and answers
I sell my products from Switzerland: what do I need to do?
The CRA and the other EU regulations apply to every product placed on the EU market, whatever the manufacturer’s country. A Swiss company that exports to the EU must therefore comply. Switzerland often aligns its rules with the EU: for example, it has taken over the cybersecurity requirements of the Radio Equipment Directive, applicable since 1 August 2025.
Preparing early secures market access and strengthens the security of your products, which customers increasingly expect.
What about products already on the market?
The requirements apply to products placed on the market from the date of application of each regulation. A product placed on the market before that date remains subject to the rules in force at that time, for example the Machinery Directive 2006/42/EC. Every new unit placed on the market after the date of application, however, must meet the new requirements. For the CRA, the reporting obligation applies since 11 September 2026 to all products concerned, including those placed on the market earlier. Start your compliance work now to be ready in time.
Do I need to comply with several regulations?
Yes, depending on the nature and functions of your product. A machine with digital elements can fall under both the Machinery Regulation and the CRA; connected radio equipment also falls under the RED. If your customer operates critical infrastructure, it must also comply with the NIS2 Directive and will ask you for guarantees.
Because these scopes overlap, an applicability analysis at the start of the project avoids duplicated work. Our experts help you define one approach for all requirements.
Are software and SaaS covered by the CRA?
Software placed on the market as a product, for example an app or firmware, is covered by the CRA. A service delivered purely remotely (SaaS) is not a product and falls rather under the NIS2 Directive. However, a remote data processing solution that a product needs to perform its functions, such as the cloud backend of a connected device, is part of that product and falls within the scope of the CRA.
For an analysis of your case, contact our experts.
How CertX supports you
Our cybersecurity experts support you on your way to compliance:
- Applicability and gap analysis: identify the regulations that apply and assess your current situation against their requirements.
- Training: raise awareness and train your managers and engineers, for example with our Red Belt courses on IEC 62443 and the CRA training of SGS Academy.
- Preparation for conformity assessment: classify your product and prepare the technical documentation and evidence for CE marking.
- Assessment and certification: assess and certify your products and processes against recognised standards such as IEC 62443-4-1, IEC 62443-4-2 and EN 18031.
Write to us at cybersecurity@certx.com or visit our Cybersecurity page.